 Ask KS-Mitra
Social engineering is a way of tricking people instead of hacking machines. Attackers mislead someone into sharing sensitive information, giving access to a system, or doing something that weakens security. They rely on human psychology, trust and everyday weak spots to get past ordinary security controls. This kind of trickery isn't new. Technology has just made it faster, cheaper and much easier to do at scale. That's why social engineering risk management matters as much to a bank customer checking their phone as it does to the bank itself.
What Is Social Engineering in the Digital World?
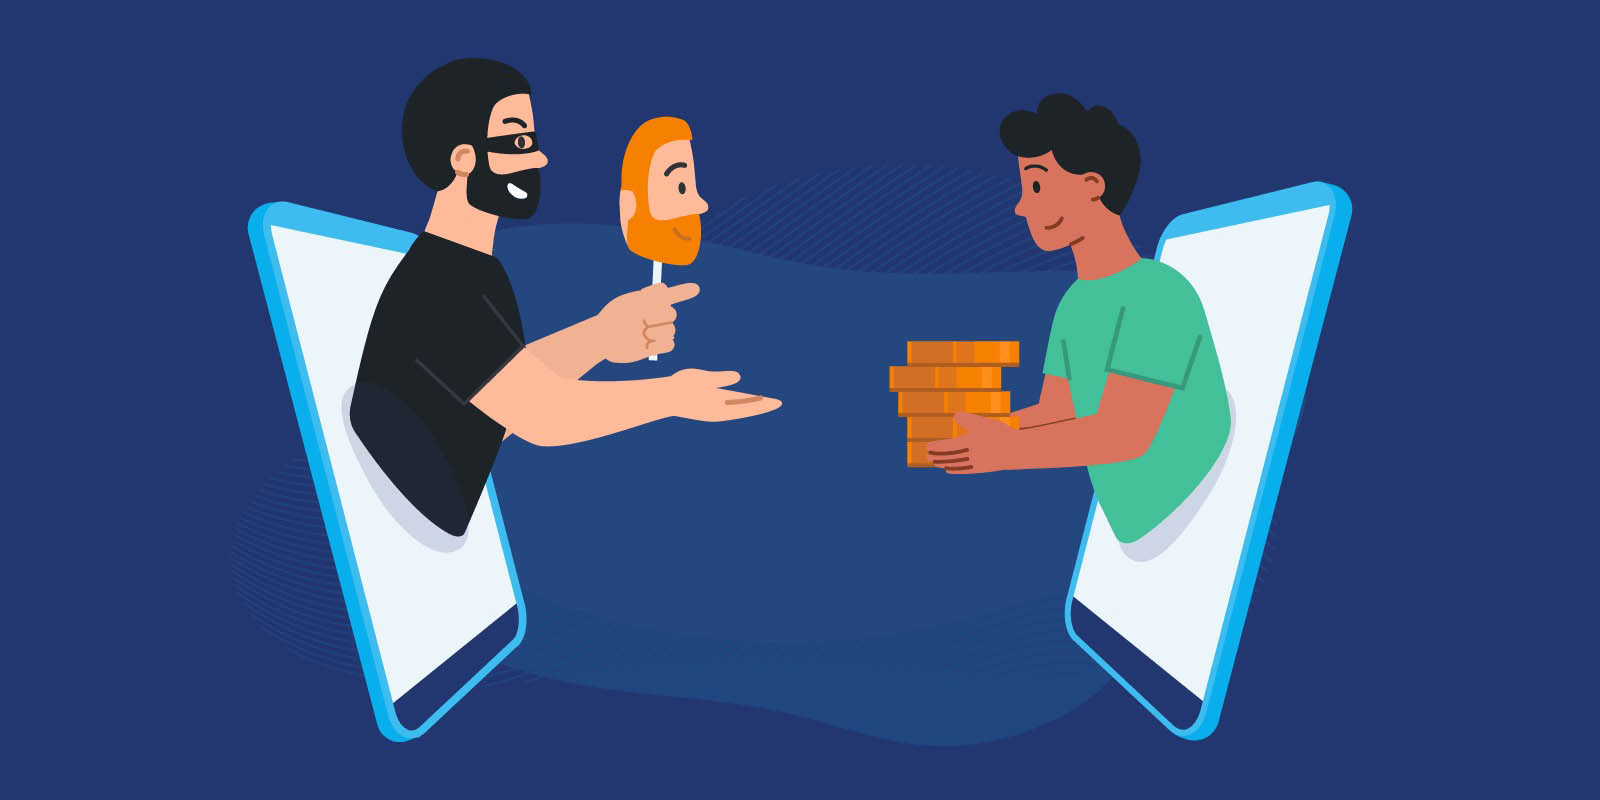
Online, social engineering usually works in one of two ways:
- Using manipulation to get into an IT system. Here the real target is the system itself. For example, a scammer might pose as someone you trust over the phone and get you to visit a malicious website that infects your computer.
- Using IT tools to set up manipulation with a goal outside IT. A common example is a phishing message that steals your banking password so the attacker can take money from your account.
This article covers what social engineering is, the forms we see most often today, the risks it creates and how to manage them.
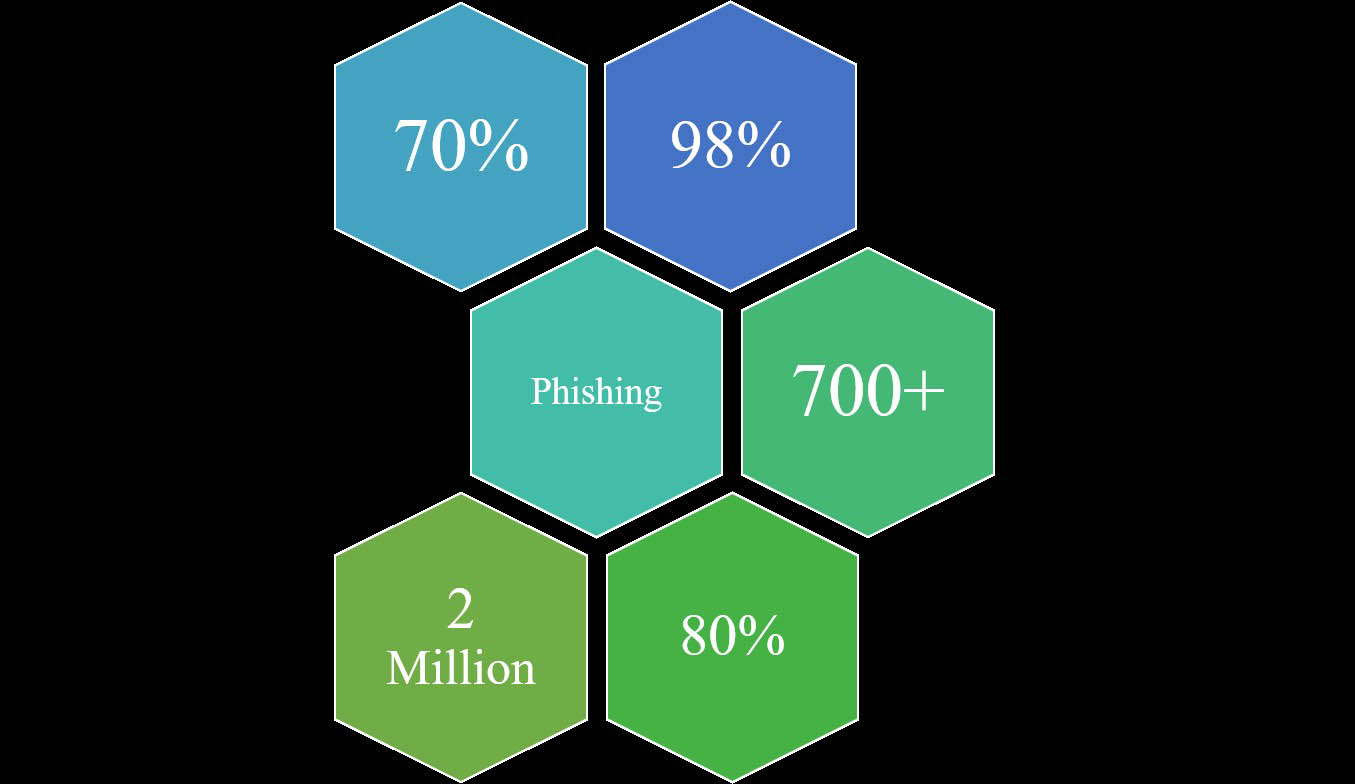
Current Statistics of Social Engineering
Common Types of Social Engineering Attacks
Two types of social engineering are especially common right now.
What Is Phishing?
Phishing is an attack used to steal user data such as login details and card numbers. It starts when someone opens an email, instant message or SMS that looks like it came from a trusted source.
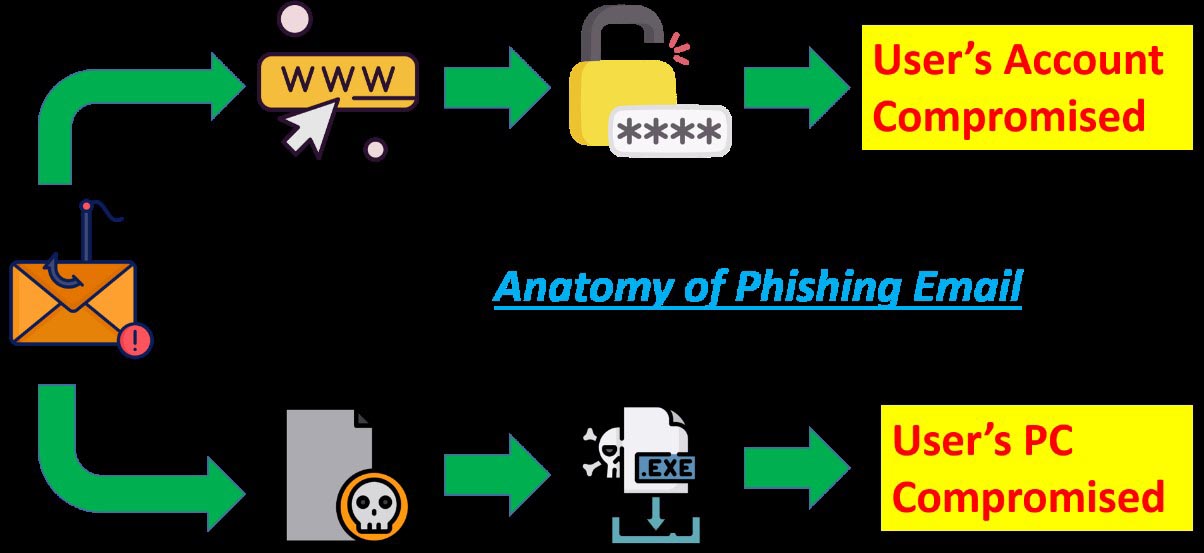
The message pushes the reader to click a link. That link might install malware, or it might open a fake website that looks just like the real one and asks for account details. Either way, the result is a compromised device, a compromised account or both.
What Is Vishing?
Vishing, short for voice phishing, happens over the phone. The attacker calls the victim and uses social engineering tactics to get personal information that opens the door to their financial accounts.
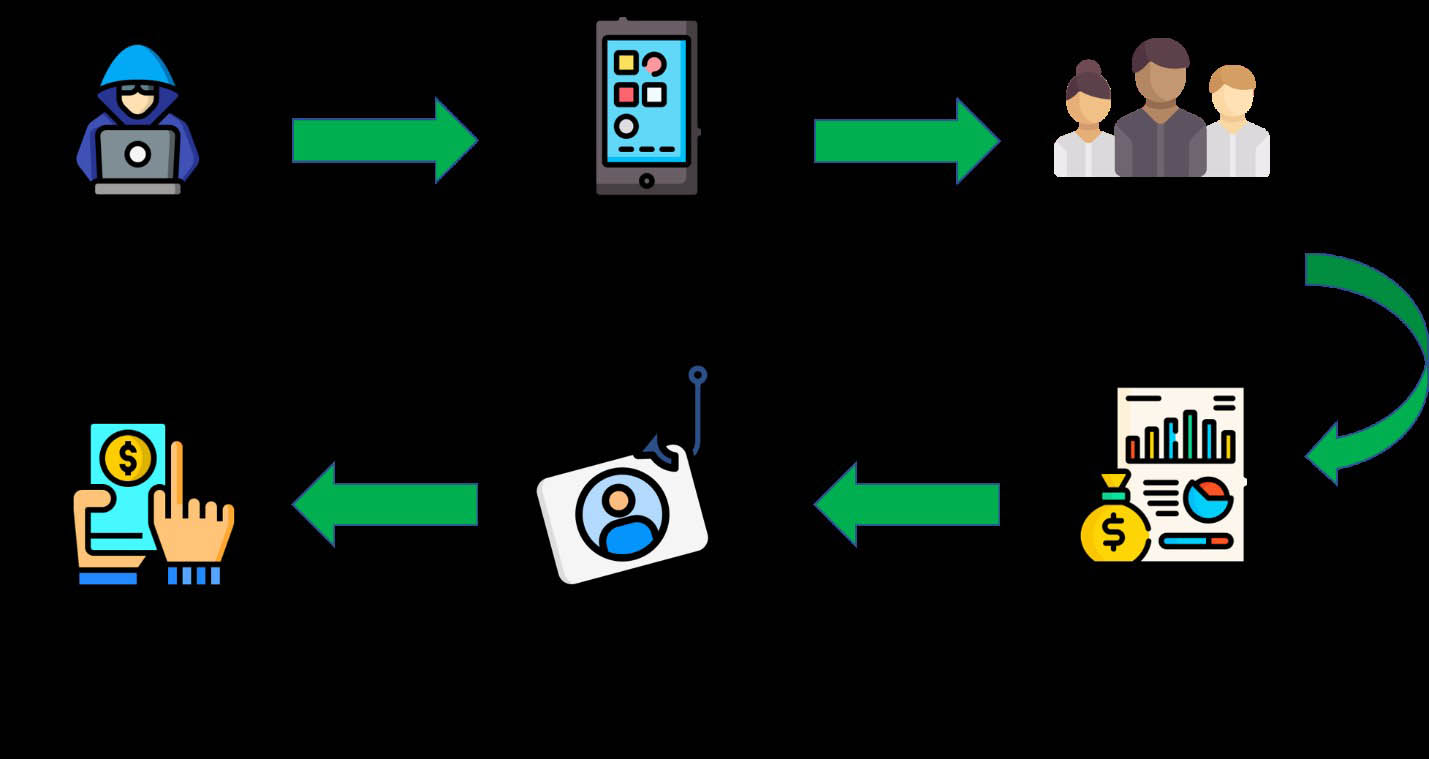
In Nepal, this is one of the most common scams right now. Fraudsters call bank customers, claim to be bank staff and ask for the account number and OTP "to update your KYC." The figure above shows how a typical vishing attack plays out.
A simple rule: a genuine bank employee has no reason to ask for your OTP, PIN or password. If a caller asks for any of these, hang up.
Warning Signs to Watch For
- Pressure to act right away ("your account will be blocked today")
- Requests for your OTP, PIN, password or full card details
- Links that look almost right but have small spelling changes
- Calls or messages you didn't expect, especially the about KYC, refunds or prizes
- A caller who gets annoyed when you say you'll call the bank back yourself
Risks and Impact of Social Engineering
The damage from social engineering isn't limited to money lost or data leaked. Victims often feel stressed, anxious or violated afterwards, and that toll is real too. Here are the main risks and what they lead to.
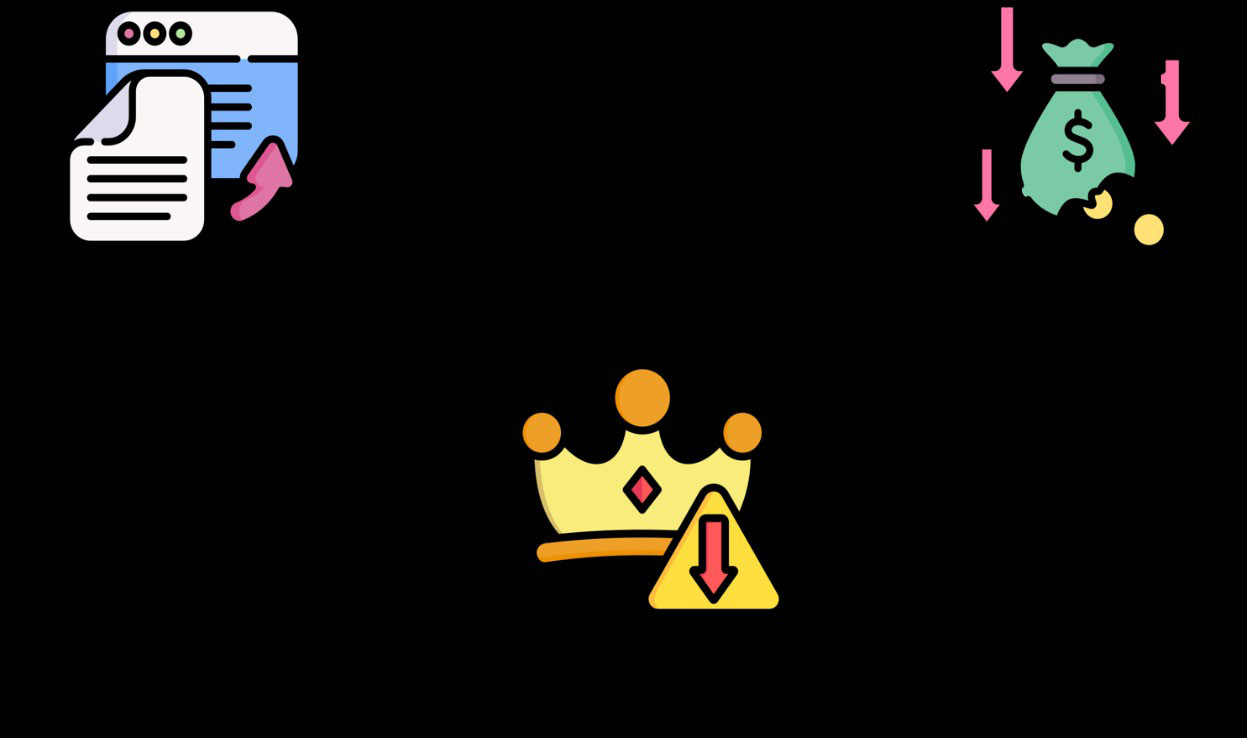
Information Disclosure
Most attacks aim to get sensitive information: personal details, login credentials, financial data or confidential business data.
- Loss of sensitive data: Attacks can expose personally identifiable information (PII) or intellectual property, which can lead to financial fraud, identity theft or other crimes.
- Identity theft: With enough personal details, an attacker can pretend to be you and commit fraud in your name. The financial and reputational fallout can last a long time.
Financial Losses
Many attacks are simply about money, whether they target one person or a whole organization.
- Fraudulent transactions: Once someone is tricked into sharing payment details, the attacker can move money out, causing losses for individuals and businesses.
- Business email compromise (BEC): Using email spoofing or impersonation, attackers convince staff to make unauthorized wire transfers or share financial information. For a business, the losses can be very large.
Reputational Damage
A successful attack can seriously hurt the reputation of a person or an organization.
- Loss of brand and customer trust: Customers may leave, business opportunities can disappear, and the brand takes a hit that's hard to repair.
- Legal and regulatory consequences: In tightly regulated sectors like banking, a breach can bring penalties, lawsuits or investigations into privacy failures and weak security controls.
How to Manage Social Engineering Risk
Once people and organizations understand these risks, they can act early to close the gaps attackers use. Below are the key measures that make a real difference.
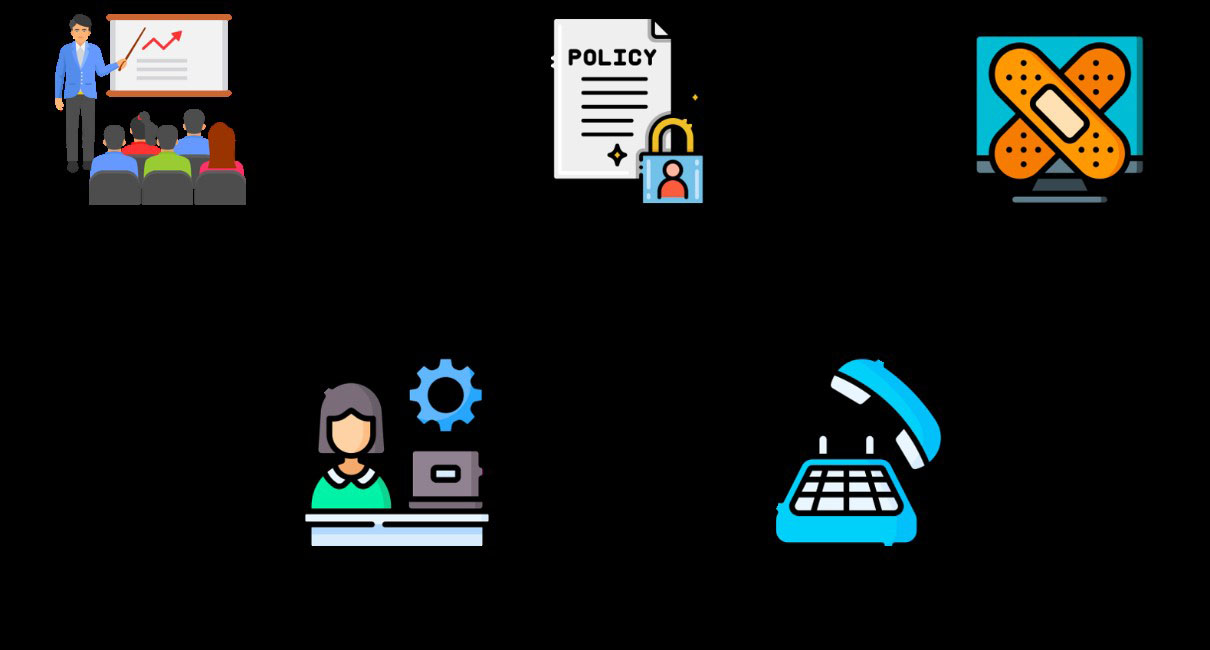
Security Awareness and Training
Employees and customers both need regular awareness training. Staff should learn how social engineering works and what it can cost. Customers benefit from short educational material, blog posts and FAQs on these topics. Technology can't catch everything, so awareness is the last line of defense. It helps people notice red flags, report them quickly and stay alert.
Strong Password Policies
Organizations should enforce strong password policies for both internal systems and customer-facing services. Complex passwords, regular rotation and two-factor authentication together make it much harder for fraudsters to get in.
Secure IT Infrastructure
Both organizations and individuals should keep devices and systems patched so attackers can't exploit known weaknesses. On mobile phones, install apps only from official app stores, and scan any app that comes from somewhere else. For your bank, use the official KS iMobile app rather than links sent by text or social media.
Vendor and Third-Party Management
Many organizations outsource services to vendors to work more efficiently. But third-party access can also become a route for data loss. Every organization should review the security protocols vendors follow before giving them access to systems or sensitive data, and carry out proper due diligence. You can read more about this wider approach in the ecosystem of risk management.
Fraud Reporting and Response
Customers and employees need clear, easy-to-find ways to report anything suspicious straight away. Every report should be reviewed promptly and acted on. People also need step-by-step guidance on limiting the damage and recovering any losses.
What to Do If You've Been Targeted
- Stop all contact with the caller or sender.
- Contact your bank right away through its official contact details and ask it to block your card or account if needed.
- Change your passwords and mobile banking PIN.
- Report the incident to the Cyber Bureau of Nepal Police.
- Keep screenshots, phone numbers and messages as evidence.
For more everyday safety tips, see our guide to digital transactions in Nepal.
Frequently Asked Questions
What is social engineering in banking?
Social engineering in banking means tricking customers or staff into giving away sensitive information such as account numbers, passwords, PINs or OTPs. Attackers usually pretend to be bank staff, a government office or a trusted company, then use urgency or fear to get the victim to act before they think it through.
Will my bank ever ask for my OTP over the phone?
No. A genuine bank employee has no reason to ask for your OTP, PIN or password by phone, SMS or email. An OTP exists only to confirm a transaction that you started yourself. If someone asks for it, treat the call as fraud, hang up and contact the bank through its official number.
What is the difference between phishing and vishing?
Phishing uses written messages, such as emails, SMS or chat messages, to trick you into clicking a fake link or sharing details. Vishing does the same thing through a phone call. Both rely on impersonation and pressure, and both usually aim to steal login details or banking information.
How can I protect myself from social engineering attacks?
Never share your OTP, PIN or password. Check unexpected requests by calling the organization back on its official number. Turn on two-factor authentication, install apps only from official stores and keep your phone updated. If a message feels rushed or too good to be true, stop before you click anything.
What should I do if I shared my OTP with a scammer?
Call your bank immediately and ask it to block the card or account. Change your mobile banking PIN and passwords, then report the case to the Nepal Police Cyber Bureau. Save the caller's number, any messages and screenshots, because this evidence helps with the investigation and any recovery.
Why is social engineering so effective?
It targets people instead of technology. Firewalls and antivirus software can't stop someone who willingly shares their own password. Attackers use trust, fear, urgency and helpfulness to push people into quick decisions. That's why regular awareness training is one of the strongest defences.
Conclusion
Social engineering is a constant, changing threat that gets past technical controls by targeting human weaknesses. The tactics keep changing, but the main dangers stay the same: leaked information, unauthorized access, financial loss and damage to reputation. Good social engineering risk management starts with understanding these risks. When people and organizations know what to look for, they can close the gaps attackers depend on. Regularly reviewing risk policies, training staff and customers, and strengthening technical controls are what keep that defence strong over time.
Author: Bidhan Koirala, Head: IT/Digital Banking, Kamana Sewa Bikas Bank Limited
Further reading: Nepal Rastra Bank and CISA.